πŸ” Search
Sign in to post
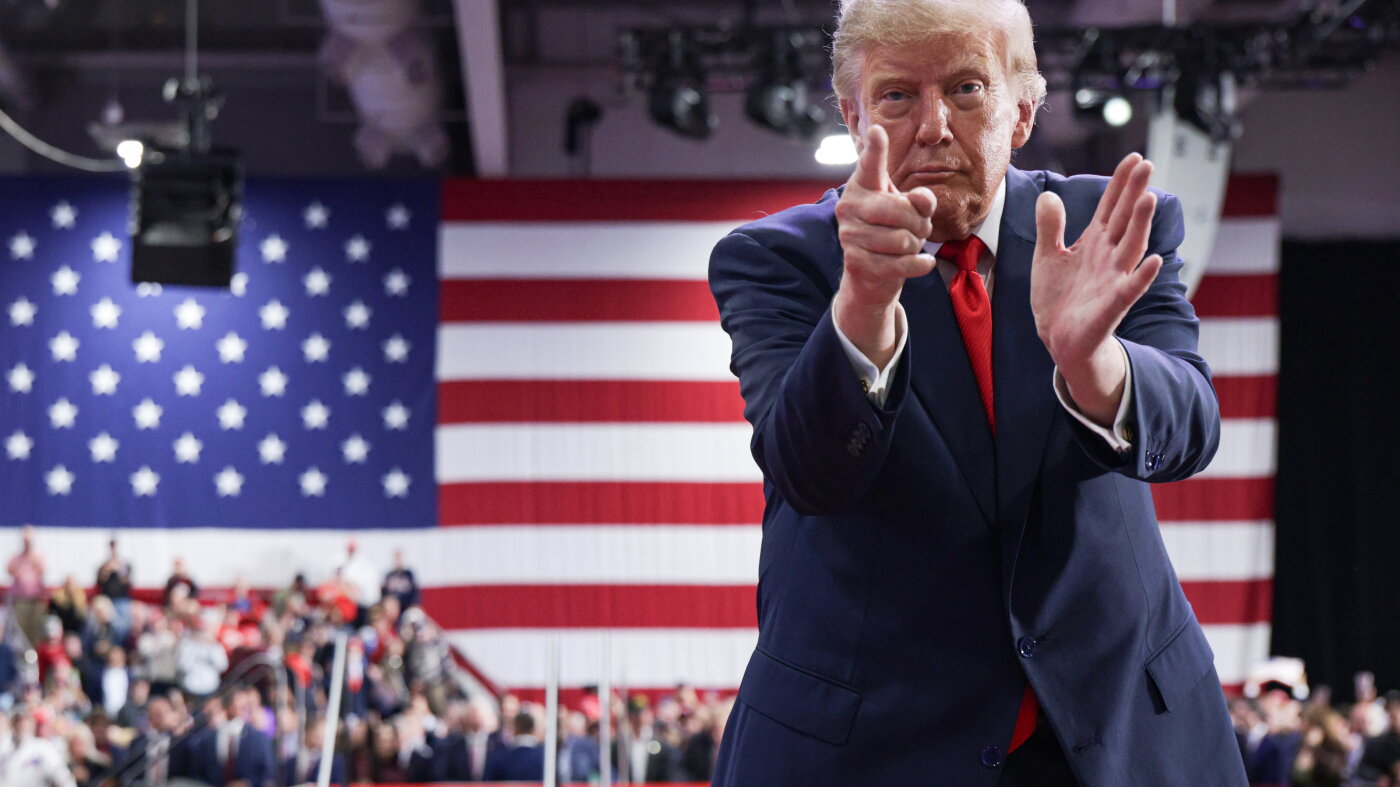
Government spent $10 million on pro-Trump ads after president said super PAC would fundhttps://www.npr.org/2026/10/12/nx-s1-5998976/pro-trump-ads-taxpayer-funds-federal-judge

Nearly $22 million in taxpayers funds has been spent to air the ads, with nearly half spent after Trump promised to fund what the White House calls public service announcements through his super PAC.
β†—
Show HN: Crowdsource Square Packingshttps://square-packing.franciscouzo.com

Square packing problems have been quite trendy the last month, with some viral X and Reddit threads. I hold a few records at it, but the main limitation right now is computation, that's why I created a website to crowdsource its computation. Comments URL: https://news.ycombinator.com/item?id=50060327 Points: 1 # Comments: 0

Show HN: How to beat Pac-Man with a text classifierhttps://jeffyclassify.com/blog/pacman

Article URL: https://jeffyclassify.com/blog/pacman/ Comments URL: https://news.ycombinator.com/item?id=50057795 Points: 1 # Comments: 0

Tensorlake npm Package Compromised to Deliver Shai-Hulud Credential-Stealing Wormhttps://thehackernews.com/2026/10/tensorlake-npm-package-compromised-to.html

The npm package known as "tensorlake," a TypeScript software development kit (SDK) for Tensorlake applications, sandboxes, and cloud services, was compromised as part of a ChainDrop / Shai-Hulud supply chain attack. The malicious version 0.5.144 "contains obfuscated malware that harvests credentials, exfiltrates secrets, establishes persistence, and executes remotely supplied code," Socket said

Eight Malicious npm Packages Downloaded 40,767 Times Deliver Overlord RAT and Stealerhttps://thehackernews.com/2026/10/eight-malicious-npm-packages-downloaded.html

Cybersecurity researchers have disclosed details of a long-running npm supply chain malware campaign that pushes information stealers and remote access trojans (RAT) to compromised hosts. The campaign has been codenamed MALFEX by CloudSEK and Checkmarx. The activity is assessed to be the work of a lone threat actor who appears to have published 12 packages since August 2023, eight of which have

One Packet Can Crash OT Servers in Industrial Sectorshttps://www.darkreading.com/ics-ot-security/one-packet-crash-servers-tdengine

A high-severity vulnerability affects the TDengine time-series database used across industrial, IoT, energy, and automotive environments, and orgs should patch right away.

β†—

0trust.social media

Loading your media...

Pick a GIF β€” Giphy

Loading GIFs...